BlueDot IT work

Proof, not a repository dump.

Two flagship examples show the problem, the work, the evidence, and the result. They are public engineering artifacts—not disguised client testimonials.

Request a scoped review

The primary work page stays focused on the clearest security and AI automation examples. The broader public repository archive remains available separately.

Security engineering

security-middleware

Open public repository
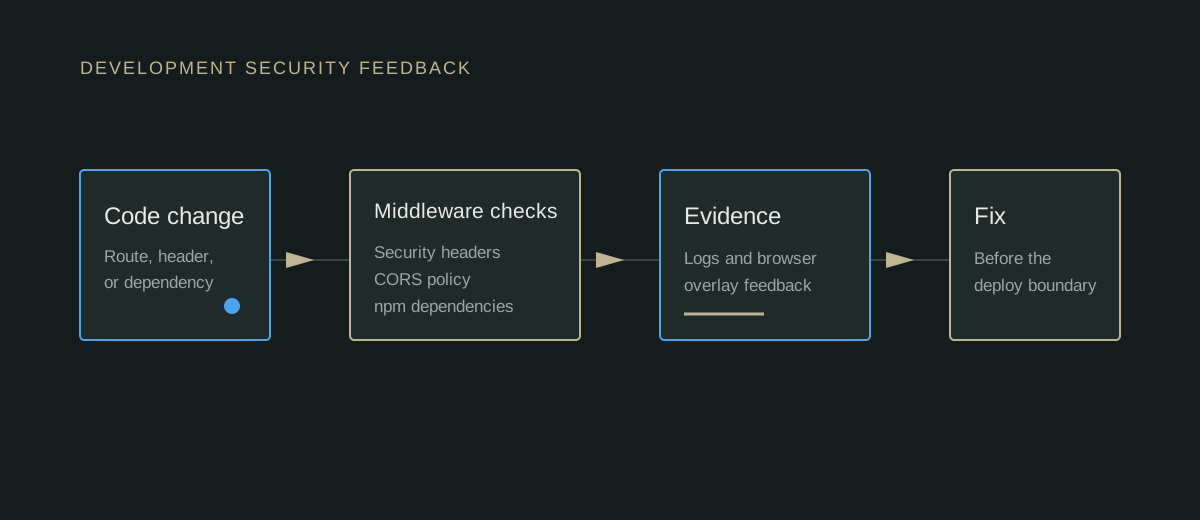
Diagram showing a code change moving through header, CORS, and dependency checks before developer feedback.
Public artifact: a developer-facing security feedback flow.

Node.js and Next.js development middleware that checks security headers, CORS, and npm dependencies and reports findings through logs or a browser overlay.

Problem
Security checks are often separated from the place where a developer is making the change, so findings arrive late and without context.
Work
BlueDot built middleware that checks headers, CORS, and npm dependencies and reports findings through logs or a browser overlay during development.
Evidence
The public TypeScript repository contains the middleware, checks, and developer feedback path for inspection.
Result
A class of application-security concerns becomes visible while the person who can fix it still has the relevant code and context.
Built withTypeScript · Node.js · Express · Next.js

Operational safeguards: Development middleware surfaces issues; it is not a substitute for a complete security review or production control set.
AI automation + security

GhostMCP

Open public repository
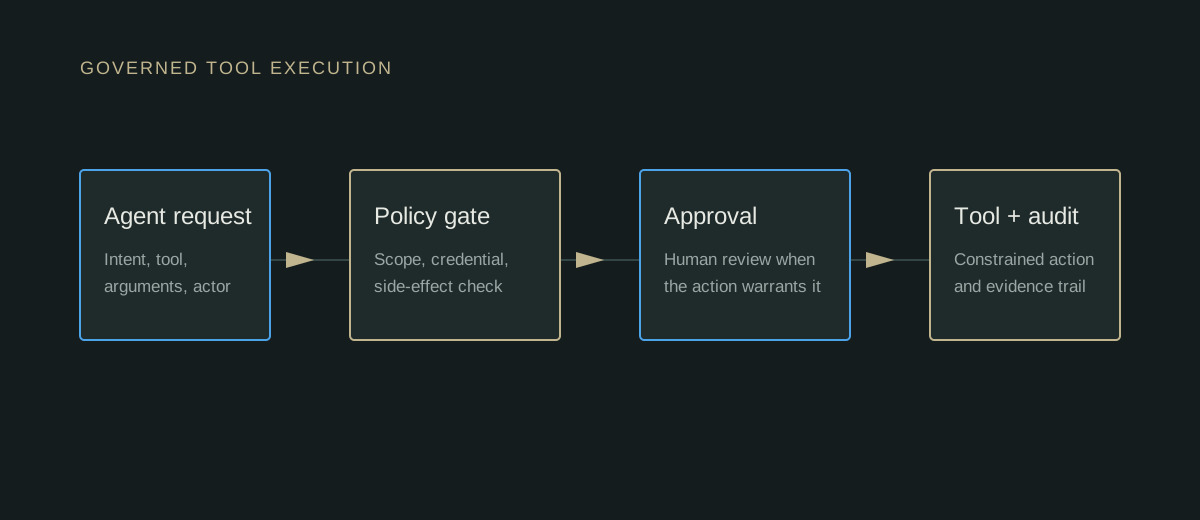
Diagram showing an agent request passing through policy, approval, execution, and audit evidence stages.
Public artifact: a governed tool-execution flow.

Beta security-focused MCP server for authorized assessments with policy-guarded tools, curated scanners, workflows, dashboards, scheduling, and audit logging.

Problem
An agent that can call useful tools can also create side effects. Permission, approval, credential, and audit decisions need to be explicit.
Work
GhostMCP combines policy-guarded tools, curated workflows, scheduling, dashboards, and audit logging for authorized security assessments.
Evidence
The public beta repository documents the server, tool controls, workflows, and audit trail. It is not presented as a universal safety guarantee.
Result
The design makes tool authority and operator oversight visible enough to review before an agent is allowed into a real workflow.
Built withPython · MCP · FastAPI · SQLite

Operational safeguards: The repository describes a beta release; restricted deployment, operator control, and written authorization remain necessary.

Open source archive

The rest of the lab stays inspectable.

Additional public systems cover agent runtimes, model routing, vulnerability intelligence, and reproducible evaluation. They are useful technical evidence, but they do not represent private client outcomes.

Browse the open-source archive
Next step

Need the same discipline applied to your system?

Tell BlueDot what is failing, what is already in place, and what outcome would make the work useful.

Request a scoped review